
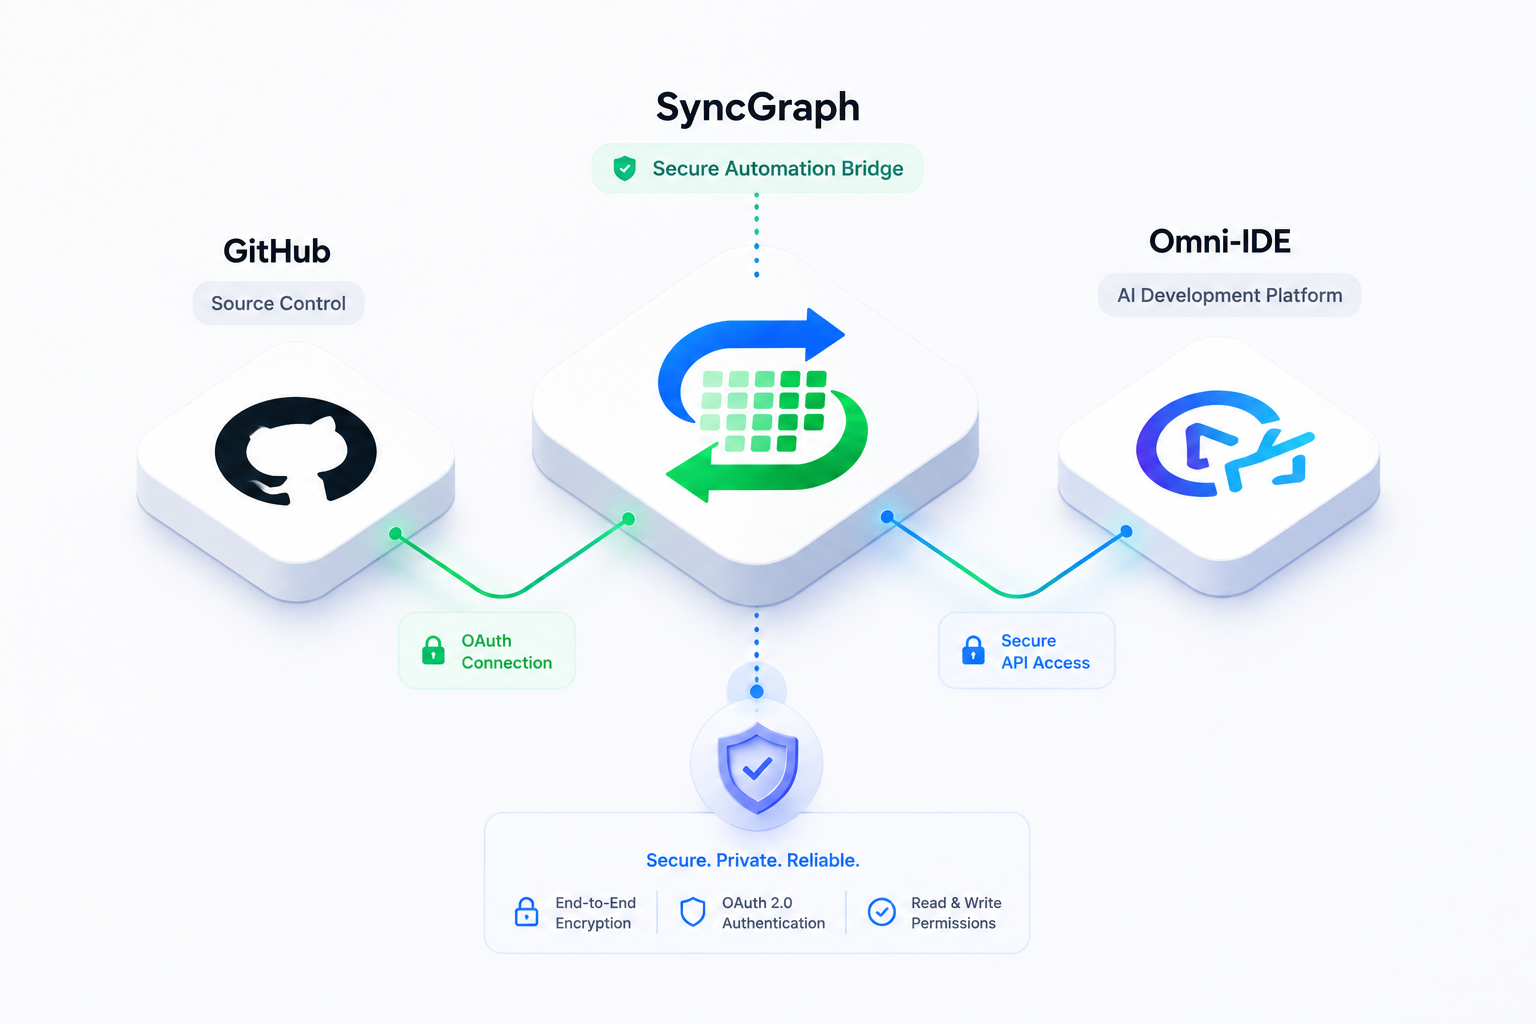
Designing Secure GitHub OAuth Workflows
Protecting OAuth credentials is fundamental to the architecture of SyncGraph. Since we push code on your behalf, we handle your tokens with the highest security standards.
Minimum Viable Scopes
We request only the `repo` scope during authentication. We do not request access to read your private emails, manage your organizations, or delete repositories.
Credential Protection (AES-256-GCM)
All GitHub tokens are encrypted at rest using AES-256-GCM:
- **Key Derivation:** PBKDF2 with a unique salt.
- **Encryption Mode:** GCM (provides authenticated decryption).
This guarantees that even with physical database access, your tokens remain cryptographically secure.